GitHub App is live.PR scans without wiring CI by hand.Install it ->

An extremely fast security scanner, written in Rust.

Cross-file taint tracking, 200+ built-in rules, and a post-quantum crypto audit in a single binary. Free and open source.

Scans in milliseconds

Written in Rust, with no database to build.

Scanning express, from scratch.· 141 files · 19x faster
foxguard
0.000s
Semgrep
0.00s
OpenGrep
0.00s
Scanning flask, from scratch.· 83 files · 20x faster
foxguard
0.000s
Semgrep
0.00s
OpenGrep
0.00s
Scanning gin, from scratch.· 99 files · 15x faster
foxguard
0.000s
Semgrep
0.00s
OpenGrep
0.00s

foxguard 0.8.1 built-ins vs Semgrep 1.156 & OpenGrep 1.22 (--config auto, identical findings) · median of 3 runs, Apple Silicon · bars animate at true measured wall-clock time ·full comparison vs CodeQL, Snyk & SonarQube →

Cross-file taint analysis

foxguard tracks untrusted input across files in eight languages — Python, JavaScript, Go, Java, Ruby, PHP, C#, and Kotlin — linking a source in one file to a sink in another in 0.03 seconds.

views.py
from . import queries

def search(request):
    name = request.GET["name"]
    return queries.run_query(name)
queries.py
def run_query(name):
    cur = db.cursor()
    cur.execute(
        "SELECT * FROM users"
        " WHERE name = '" + name + "'"
    )
request.GETviews.pyqueries.pycursor.execute

Dataflow traces

--explain prints the full source-to-sink path, file and line, plus a fix.

Confidence-scored

Findings are ranked by dataflow depth, so the most certain ones surface first.

Branch diffing

foxguard diff main shows only findings your branch introduces.

Built for your terminal

Readable scan output, plus an interactive TUI. Run foxguard tui . to browse findings, read dataflow traces, and dismiss false positives.

terminal
foxguard
src/auth/login.js · 2 issues
CRITICALUntrusted input reaches `db.query`
js/taint-sql-injection (CWE-89)line 14:5
db.query("SELECT * FROM users WHERE id = '" + req.params.id + "'")
Fix: Use parameterized queries
HIGHHardcoded JWT secret
js/jwt-hardcoded-secret (CWE-798)line 8:1
const JWT_SECRET = "super-secret-prod-key"
app/views.py · 1 issue
CRITICAL`request.GET` reaches `cursor.execute`
py/taint-sql-injection (CWE-89)line 52:12
cursor.execute("SELECT * FROM users WHERE id = '%s'" % user_id)
Fix: Use parameterized queries
3issues1,204 files · 0.14s
2 critical1 high
foxguard tui .
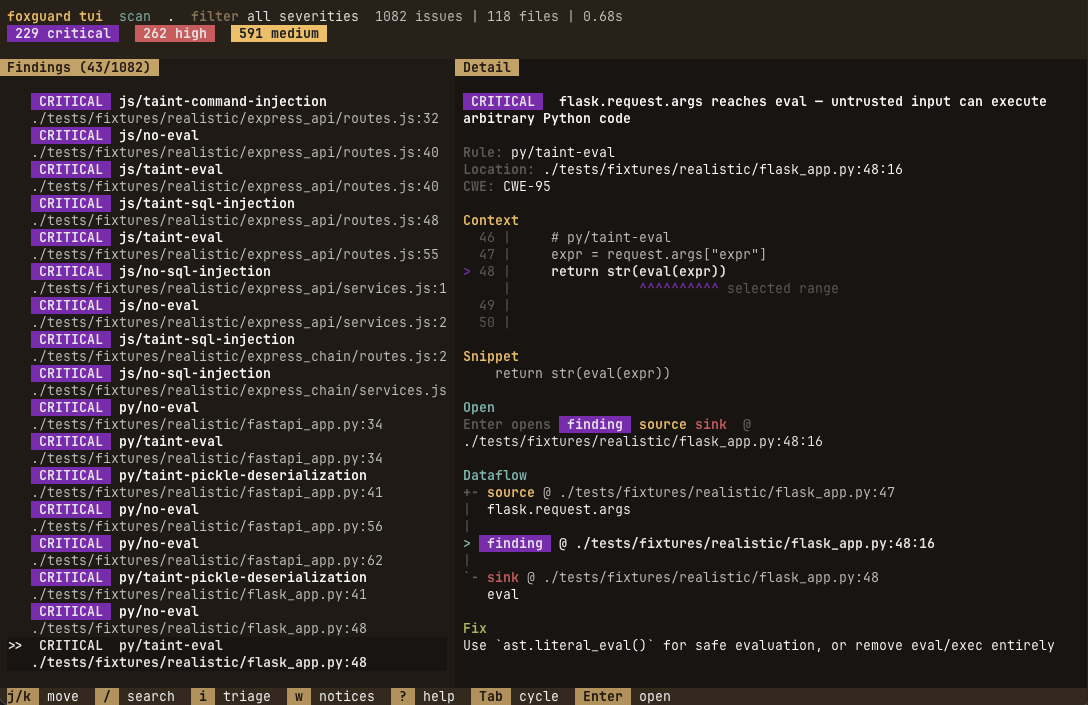
foxguard TUI showing the findings list on the left and the full dataflow detail for a selected SQL injection on the right
$ npx foxguard tui .

Framework-aware by default

Built-in rules understand Express, Django, Flask, and Spring, so a safe idiom won't raise a false alert.

Express / Node
Flask / Django
Gin / net/http
Rails / Ruby
Spring / Java
PHP / Laravel
Rust
C# / .NET
Kotlin / Ktor
Swift / iOS

Cross-file taint tracking

Trace untrusted input across file boundaries. Source in one file, sink in another — the engine connects them.

Branch diffing

foxguard diff main shows only new findings your branch introduces. No noise from existing code.

PR review comments

--github-pr posts findings as inline review comments directly on pull requests.

Fix suggestions

Every taint finding includes a concrete fix with safe code patterns. --explain shows full dataflow traces.

Secrets scanning

Detect leaked credentials and private keys with redacted output in the same tool.

Semgrep YAML bridge

Load existing Semgrep/OpenGrep rules with --rules. Loads ~98% of the public Semgrep/OpenGrep registry, parity-tested in CI.

Semgrep compatibility

Load your existing rules with --rules — foxguard loads ~98% of the public registry, parity-tested in CI.

patternpattern-regexpattern-eitherpattern-notpattern-not-regexpattern-insidepattern-not-insidepatterns (AND)metavariable-regexpaths.include/excludeFull Semgrep syntax

Post-quantum crypto audit, built in

One command flags RSA, ECDSA, ECDH, DH, and DSA across five languages, web-server configs, and six lockfile formats.

$ foxguard pqc .

CNSA 2.0 deadlines

Every finding carries its CNSA 2.0 migration deadline. Know what moves, and by when.

Migration readiness

A readiness score: how exposed you are, and where to start.

CycloneDX CBOM

foxguard pqc . --format cbom exports a CycloneDX cryptography bill of materials.

Try it on your codebase

One command, no setup.

foxguard secrets . also catches leaked AWS, GitHub, Stripe, Slack, and private keys, redacted by default.